Security Incident Affecting Your Double Counter Data
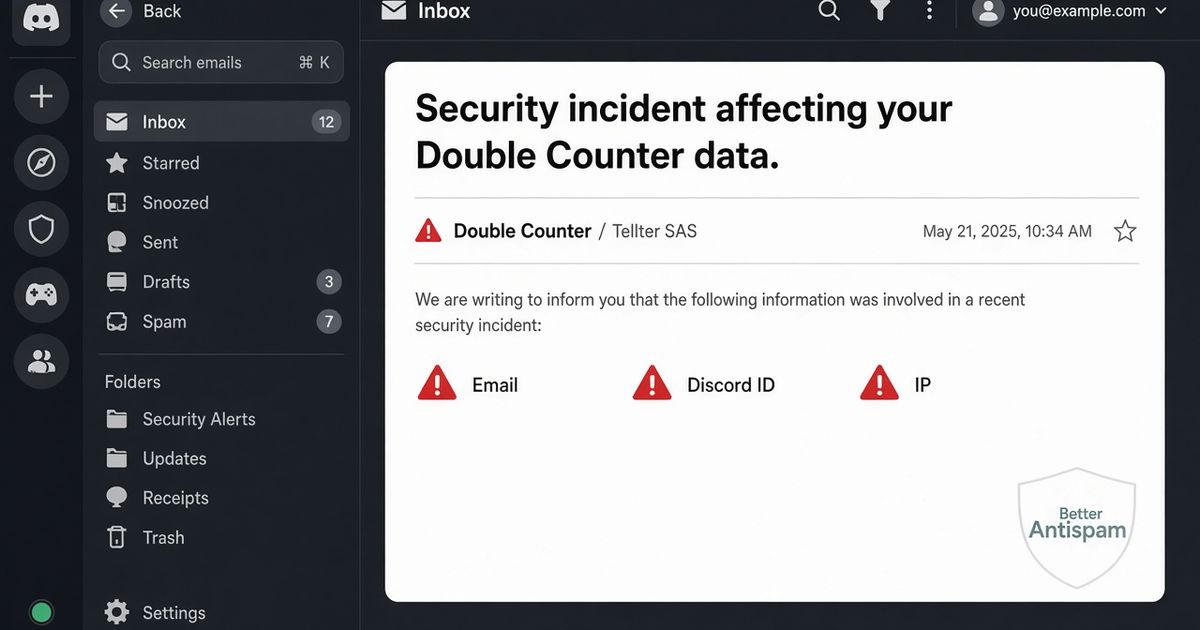
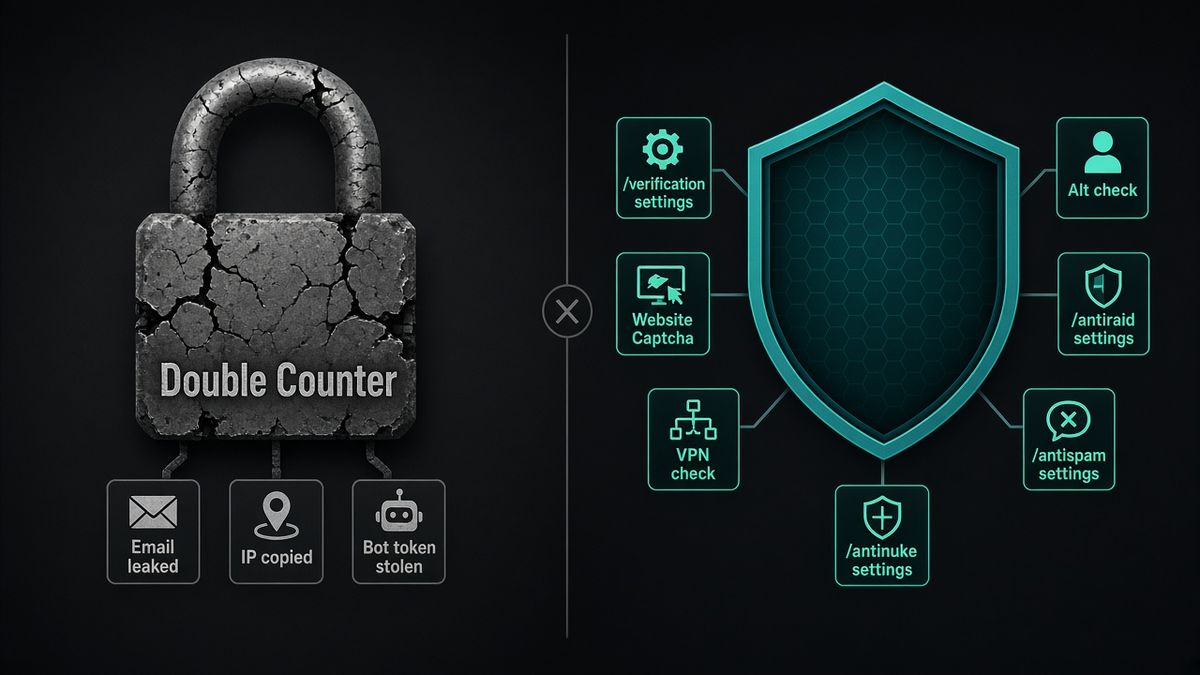
Yes, the email titled Security incident affecting your Double Counter data is real. Tellter SAS, the French company behind Double Counter, is notifying people whose records sat in a database an attacker copied on 4 October 2026. The way in was a public Metabase install on a retired server. If you still use that bot as your only gate, take it off and put BetterAntispam on: /setup, then /verification settings (Administrator). Website Captcha, VPN / proxy / Tor checks, and alt detection live in that panel. Antispam, antiraid, and antinuke are the same bot. I maintain it. We do not sell a people-search on verify clicks. No bot is unhackable.
Editorial disclosure: This guide is published by BetterAntispam. We recommend BetterAntispam when you want verification plus chat, raid, and nuke protection in Discord slash commands. Incident facts come from Double Counter’s own report (updated 21 October 2026), their notification email, Have I Been Pwned, and The Verge. Privacy criticism is attributed to their docs, Reddit, and YouTube, not a court verdict.
TL;DR: People googling security incident affecting your Double Counter data, double counter security incident, and is the double counter email real got a GDPR notice. Email, Discord ID, username, IP, user agent, and linked accounts may be in the copy. Passwords and Discord OAuth tokens were never stored, according to them. The email underplays the rest of the incident: a stolen bot token, attacker invites in about 50 large servers, ~12 GB copied, fraudulent charges on a sibling product. Have I Been Pwned indexed published emails. Minute-by-minute writeup: Double Counter data breach. Switch: /verification settings. Comparison: BetterAntispam vs Double Counter.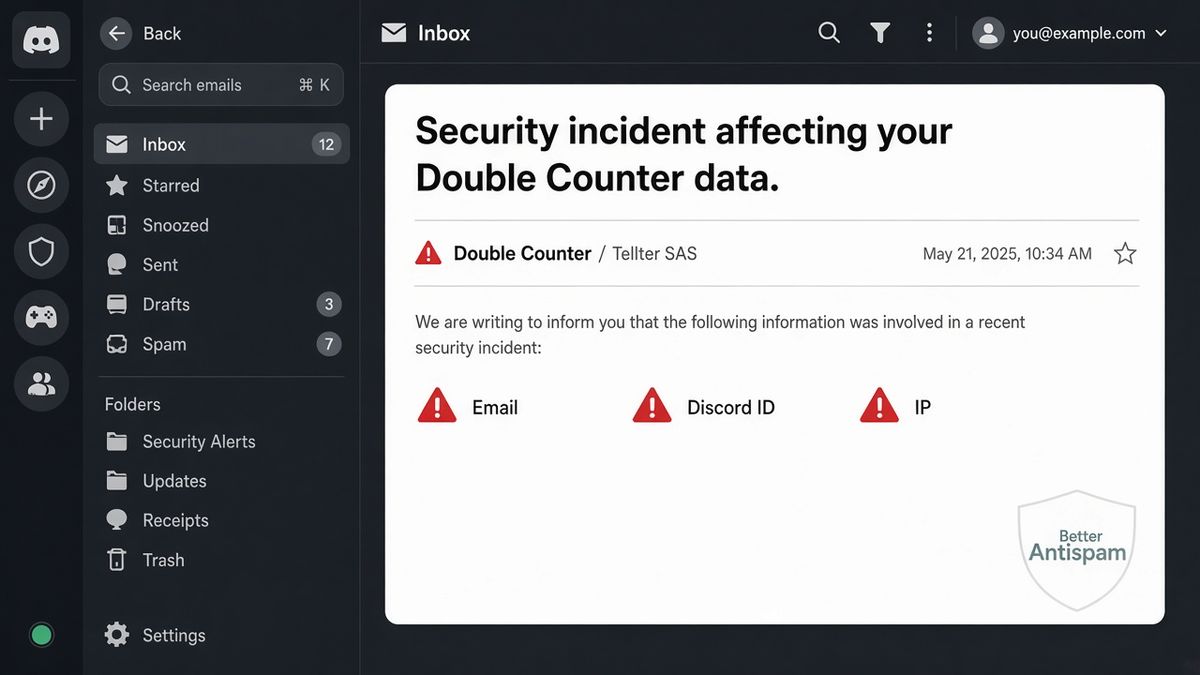
What that email actually says
The message is from Double Counter / Tellter SAS, 9 rue des Colonnes, 75002 Paris. CNIL was notified on 5 October. They filed a criminal complaint. Full report: doublecounter.gg/blog/security-incident-october-2026.
What happened, in their words: on 4 October 2026 an attacker used a vulnerability in third-party analytics (Metabase) and copied part of the database. Part of the stolen data was then published.
What they say was affected, at most: email address, Discord user ID and username, IP address and derived info, browser user agent, and linked accounts from verification. They do not know whether your row was in the published files. They say Discord OAuth tokens, account tokens, and passwords were never collected.
What they tell you to do: expect phishing that uses your email or Discord details. They will never ask for a password, Discord token, or payment by email or DM. Delete data with /privacy, or write gdpr@doublecounter.gg.
Believe the phishing warning. Do not treat the email as the whole incident. Their own report is worse, and it is public.
The email is the polite version
The notification is a data-subject letter. The incident report is the operations log. Read both.
| What the email emphasizes | What their report also says |
|---|---|
| Metabase vulnerability, database copy, published files | Retired OVH box, still on the public internet, still holding cloud admin keys |
| Your email might be in the dump | About 12 GB copied; they treat the verified-user IP table as exposed because the copy was interrupted |
| Phishing is the main risk | Stolen Discord bot token. The attacker was Double Counter in every invited server |
| We cut access and rotated credentials | Attacker invites posted in about 50 large servers. Administrator on Double Counter’s own support server |
| Not mentioned | Fraudulent charges on a sibling Atis payment account (report: about $7,331 charged, most refunded the same day) |
| Not mentioned | Verify buttons died with “The application didn’t respond in time” for hours |
Have I Been Pwned added Double Counter on 7 October 2026. HIBP’s published corpus is about 275,000 unique emails and usernames. Double Counter’s own table is larger: on the order of 1.3 million emails copied, ~27 million IP-to-Discord-ID rows partly copied, ~44 million user-agent hashes copied. Copied is not the same as posted. Posted is not the same as gone. “Contained” does not pull files off dump sites.
If you used Double Counter, Doogle, their dashboard, or their API, check HIBP. Then assume phishing mail will use your real Discord username.
What this means for you
An email plus a Discord ID plus an IP is enough to impersonate staff. “We detected an alt on your account, verify again” with a cloned page is the obvious follow-up. Linked accounts from verification are worse: a “fun” alt and a work alt on the same connection were already the product.
Consequences that last after they rotated secrets:
- Phishing. The risk they named. Treat unexpected Double Counter, Discord, or “verify now” mail as hostile.
- The graph is still a graph. IPs and user agents were stored to bind Discord IDs together. Once copied, that binding can be reused by whoever has the file.
- Household false positives become a leak. No Text To Speech already showed roommates and family on one IP looking like alts. That file now sits with attackers, not just Doogle subscribers.
- Your onboarding died the afternoon of the theft. A verify bot that is the only door cannot fail closed without locking real members out. Native Verification Levels and Pause Invites should have been behind it. Many servers had nothing behind it.
- A stolen bot token is a raid. Discord’s raid guide exists because a trusted app posting invites is how you burn a community in minutes.
I would not run a bot that needs 27 million IPs to do its job, then leaves the analytics box from the last host online.
This was not a surprise if you watched how they handle data
I am not inventing a secret history. Their published product is the privacy problem. The breach made the cost visible.
Doogle is a paid lookup of associated Discord accounts, powered by the same pipeline as verification, across more than 500,000 servers in their own writeup. The person searched is not notified. r/discordapp called that a privacy invasion a year before October. Their legal page says they do not sell stored personal data or IP addresses, and also describes Doogle as a subscription that returns associated accounts. I treat Doogle as a people-search on a verify graph. /privacy that you must repeat on every linked account, only in a server where the bot is installed, is a weak answer to “I never invited this company.”
The free verify page uses Ezoic ads unless you pay Pro. A CAPTCHA gate that funds an ad network is a choice. BetterAntispam does not put an ad network on the door.
Their getting started docs say configuration happens in a website Dashboard. Setup slash commands “do not function.” The bot is not retroactive: people already in the server are not recorded. That is a verify vendor with a web login, a global graph, and a retired Metabase box that still had production keys. The 4 October path was ordinary hygiene failure: decommissioned host, public analytics, cloud admin credentials on that host, bot token readable from a container.
Panley wrote after the incident that they were caught with data they should not have had. That is an opinion about GDPR. The CNIL file number in their report is not.
Switch to BetterAntispam
Kick Double Counter when you are ready. Then add BetterAntispam (Manage Server to invite). Leave Administrator on the invite. Run /setup (Administrator), pick a log channel, then /verification settings (Administrator). There is no website account to configure protection. Members run /verify. Staff can /force verify or /bypass (Manage Server).
Docs: documentation. Support: Discord server. Core is free. Shield is the application store. Privacy contract for the web gate: Website Captcha privacy.
The same jobs Double Counter sold, without Doogle
| Job | BetterAntispam | Double Counter |
|---|---|---|
| Website verification | Website Captcha in /verification settings: one-time betterantispam.com link, 15 minutes, Cloudflare Turnstile | Core product. Members leave Discord for a web link |
| In-Discord verify | Button (default), image CAPTCHA, math, hidden word | Not the product |
| VPN / proxy / Tor | Free Website Captcha detections you toggle (VPN, proxy, Tor, hidden VPN). Staff see a summary, not the raw IP | Documented VPN / proxy / Tor blocking |
| Alt accounts | Same device, same IP, same network, alt of a banned member, look-alike names. Local, or global for your bans | Core product plus paid Doogle search of strangers |
| Ads on the verify page | No | Ezoic on free; Pro removes ads |
| Configure it | Slash commands | Dashboard. Setup commands do not function |
| Public people-search | No | Doogle |
VPN, proxy, Tor, hidden VPN, and the alt checks above are free on Website Captcha. Shield adds extra network detections (datacenter / cloud, residential proxy, mobile, iCloud Private Relay, and others) and auto-ban for alt accounts. Correlations are stored as HMACs, pruned on a retention clock. That is alt detection for your server, not a directory you can buy.
Longer verify guide: best Discord verification bot.
The rest of the bot Double Counter is not
Verification is the door. It does not stop a join flood or a compromised admin. That is why an all-in-one stack matters if you are ripping out a specialist.
| Job | Command | Permission |
|---|---|---|
| Join raids | /antiraid settings, /raidmode enable | Administrator |
| Chat floods, caps, duplicates, scam images | /antispam settings | Administrator |
| Ads in chat and profiles | /adblock settings | Administrator |
| Compromised staff | /antinuke settings | Administrator |
| Trap channels | /honeypot settings | Manage Server |
| AutoMod ping rules | /antiping settings | Administrator |
| Channel lock | /lockdown | Administrator |
| Cleanup | /purge, /nuke, /unnuke | Administrator |
Antiraid auto-scale: under 50 members, 3 joins in 10 seconds is worth noticing and 5 is a strong signal. Manual default with auto-scale off is 5 in 10 seconds. /antinuke settings defaults off. Turn it on. Raid playbook: how to stop Discord raids. Umbrella: best Discord security bot. Feature page: verification.
Keep Wick if restore-after-wipe is why you opened a security tab. Keep Double Counter only if a paid cross-server people-search is the product you actually want. I would not.
What to do this week
- Check your address on Have I Been Pwned. Treat a miss as “maybe unpublished,” not “safe.”
- Do not click login, payment, or “re-verify” links in mail or DMs about this incident. Open Discord yourself.
- If Double Counter still holds Administrator, pull it. Check the audit log for 4 October invites posted as the bot.
- Invite BetterAntispam.
/setup,/verification settings, then/antispam settings,/antiraid settings,/antinuke settings. - If you want their copy deleted,
/privacyin a server that still has Double Counter, and email gdpr@doublecounter.gg. That does not unspread a published file.
FAQ
Is the “Security incident affecting your Double Counter data” email real?
Yes, if it matches Tellter SAS / Double Counter, points at their October 2026 report, and does not ask you to log in or pay. Real notice. Fake follow-ups will use the same subject.
Did Double Counter leak my password?
They say passwords and Discord OAuth tokens were never stored. The leak is identity and tracking data: email, Discord ID, username, IP, user agent, linked accounts.
Why am I getting this weeks later?
GDPR notices go out in batches. Have I Been Pwned listed the breach on 7 October. Mail in late October is consistent with a slow send, not proof the email is fake.
Should I keep Double Counter for alts?
Only if Doogle is the product you wanted. For VPN / alt / website CAPTCHA on your members, /verification settings covers the job without a paid global search. For spam and raids, Double Counter was never the stack.
Is BetterAntispam immune to this?
No. I will not claim that. The difference I will defend: we do not productize a 40-million-ID search engine, we do not put ads on the verify page, and Website Captcha shows staff summaries rather than a raw IP dump.
Final verdict
The email is the breach catching up with inboxes. Double Counter stored the graph, left a retired Metabase box on the internet, lost a bot token, and mailed you about phishing. If you invited them for verification, VPN, and alt blocking, BetterAntispam does that work in /verification settings and then covers the rest of the server. I would switch.
— Adam
More guides
- Double Counter Data Breach: Token Leak Explained
- BetterAntispam vs Double Counter
- Best Discord Verification Bot in 2026
- Best Discord Security Bot in 2026
- How to Stop Discord Raids in 2026
- Discord AutoMod Setup in 2026
- Discord verification feature
Sources
- Targeted attack on Double Counter’s infrastructure – Double Counter
- Double Counter Data Breach – Have I Been Pwned
- Discord users’ data was exposed in a breach at server bot Double Counter – The Verge
- Doogle docs – Double Counter
- Double Counter legal / privacy
- Isn’t this a privacy invasion? – r/discordapp
- Discord Alts Can Be Tracked Now – No Text To Speech
- BetterAntispam Website Captcha privacy
- BetterAntispam documentation
- BetterAntispam application store (Shield)